

Comp AI, an emerging leader in the cybersecurity and compliance sector, announced on Thursday the successful closure of its Series A funding round, raising an impressive $34 million. This significant investment, spearheaded by Roo Capital and Grand Ventures, propels the company’s mission to revolutionize how organizations manage their security posture and regulatory adherence, particularly in the rapidly evolving landscape of artificial intelligence. The latest capital injection brings Comp AI’s total funding to date to $37.5 million, underscoring strong investor confidence in its innovative, agentic AI platform designed to tackle complex security and compliance challenges.
The Genesis of Innovation: Lessons from a Prior Venture
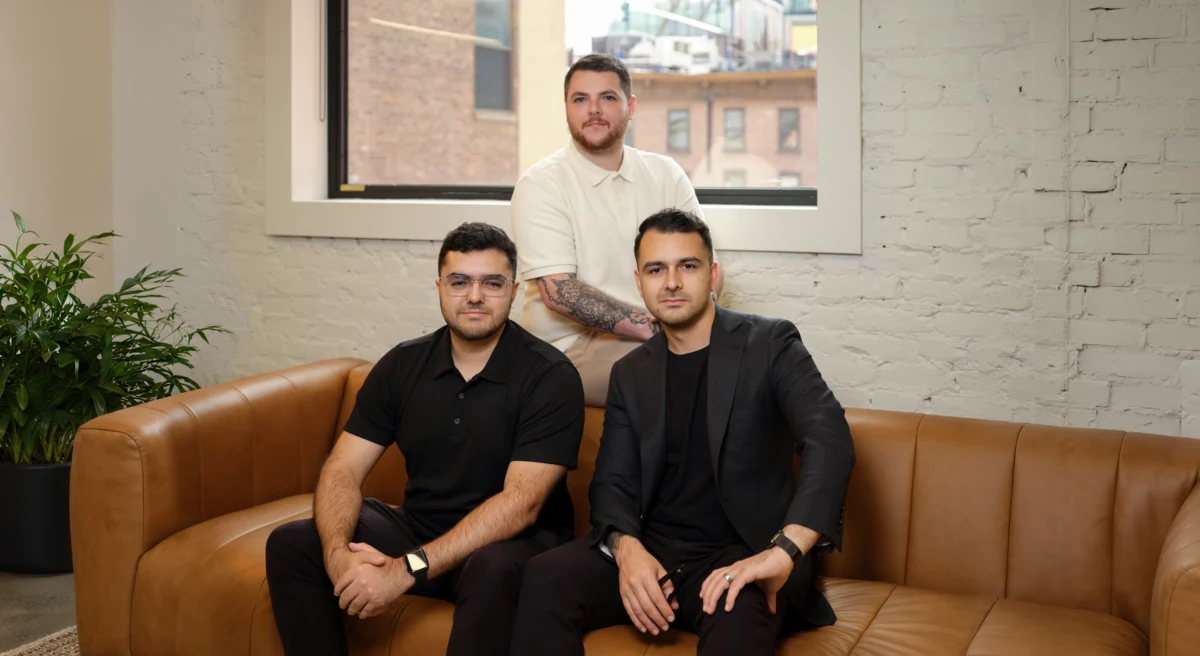
The foundation of Comp AI was laid in January of last year, a collaborative effort by three visionary founders: Lewis Carhart, who now serves as CEO; Claudio Fuentes, the Chief Operating Officer; and Mariano Fuentes, the Chief Technology Officer. The origin story of Comp AI is deeply interwoven with the founders’ prior entrepreneurial experiences and the invaluable insights gleaned from them. Claudio and Mariano Fuentes share a nearly decade-long history of joint startup ventures, a testament to their complementary expertise and shared ambition in the tech sphere. This enduring partnership led them to invite Lewis Carhart to join their previous endeavor, LeapAI, a workflow platform aimed at streamlining various digital processes.
At LeapAI, Claudio Fuentes held the CEO and co-founder roles, with Carhart contributing as the head of growth, and Mariano Fuentes serving as a senior full-stack engineer. Over its operational span of approximately two years, LeapAI demonstrated considerable market traction, successfully attracting a user base exceeding one million. Despite this impressive user adoption, the team eventually made the strategic decision to discontinue the venture. The primary challenge, as they candidly reflected, was the inability to pinpoint a "sticky enough use case to warrant continued investment." This realization, while leading to the shutdown of LeapAI, proved to be a pivotal learning experience that directly informed the strategic direction and foundational principles of their next undertaking.
The founders’ tenure at LeapAI provided profound insights across several critical domains. Firstly, they acquired hands-on experience in the practical application and integration of Large Language Models (LLMs) into product development, understanding both their immense capabilities and their operational nuances. Secondly, the experience underscored the paramount importance of identifying a highly specific and compelling problem that a product could definitively solve, a lesson that would become a cornerstone of Comp AI’s focused strategy. Thirdly, and most significantly for Comp AI’s future trajectory, the team encountered firsthand the arduous, opaque, and resource-intensive nature of the SOC 2 compliance process. This challenge became particularly acute as they sought to scale LeapAI to meet the stringent security and compliance requirements of larger enterprise clients.
Claudio Fuentes vividly recalled the frustrations of this period, stating, "It’s a very obscure process. It took us a couple of months of doing things by hand, and the whole time it meant taking our eyes off building the product." This sentiment encapsulates a pervasive challenge faced by countless technology companies: the diversion of invaluable engineering and product resources from core innovation to the demanding, often manual tasks of regulatory compliance. It was precisely this acute pain point – the tedious, time-consuming, and resource-intensive nature of cybersecurity compliance – that sparked the idea for Comp AI. With a clear problem identified and a renewed sense of purpose, the trio embarked on their new venture. This time, Lewis Carhart took the helm as CEO, a decision the founders collectively affirmed, recognizing that the core concept for Comp AI had originated from his insights into this pressing market need.
Comp AI’s Agentic Platform: A New Paradigm for Security and Compliance
Comp AI positions itself at the forefront of a new wave of cybersecurity startups, specifically engineered to address the unique demands of what is increasingly being referred to as the "agentic era." At the core of its offering is an innovative agentic platform designed to automate and streamline the often-onerous tasks associated with security and compliance. This involves leveraging sophisticated AI agents to perform functions traditionally requiring significant human intervention and specialized expertise.
The platform’s capabilities are comprehensive and directly address the inefficiencies articulated by the founders. For instance, AI agents are capable of intelligently drafting comprehensive company security policies, ensuring they align with industry best practices and evolving regulatory requirements. Beyond policy generation, these agents excel at collecting and organizing evidence for security audits, a process that typically involves sifting through vast amounts of data, logs, and documentation. By automating this meticulous evidence collection, Comp AI significantly reduces the manual effort, mitigates the potential for human error, and substantially accelerates the audit preparation timeline.
A critical distinguishing feature of Comp AI’s platform is its continuous monitoring capability. Unlike traditional, point-in-time audits that provide a snapshot of compliance at a specific moment, Comp AI constantly assesses whether a company is meeting its compliance controls. This always-on vigilance provides real-time insights into an organization’s security posture, enabling immediate identification and remediation of potential gaps or deviations from compliance standards. This proactive approach marks a significant departure from reactive, periodic compliance checks, offering a more robust, dynamic, and resilient security framework that adapts to continuous operational changes.
Furthermore, Comp AI extends its innovative application of AI to offensive security with its AI-powered penetration testing. As Carhart explained, this feature involves the platform "proactively test[ing] codebases and infrastructures for vulnerabilities." By simulating real-world attack scenarios and identifying weaknesses before malicious actors can exploit them, Comp AI enhances an organization’s defensive capabilities, moving beyond mere compliance to genuine security hardening and proactive risk mitigation. This dual approach of automated compliance and offensive security positions Comp AI as a comprehensive solution for modern cyber risk management.
The Indispensable Human Element: Augmentation, Not Replacement
Despite its strong emphasis on AI automation, the founders of Comp AI are resolute in their assertion that the platform serves as an augmentative tool, designed to empower human professionals rather than replace them. They emphatically state that the software is engineered to assist companies in meeting and maintaining security requirements, but it does not supersede the crucial role of actual independent audit reviews. Similarly, human workers remain integral to the operational workflow of Comp AI.
The founders highlight several key areas where human involvement is indispensable: onboarding the AI agents, providing context and support for controls, and maintaining the overall agentic workflow. Lewis Carhart elaborated on this collaborative dynamic, stating, "An agent might draft a policy, for example, but a person still reviews and approves it. As agents take on more consequential actions over time, we believe the level of safeguards and human approval should increase accordingly." This philosophy underscores Comp AI’s commitment to responsible AI deployment, where automation enhances efficiency while human oversight ensures accuracy, accountability, and strategic decision-making. This hybrid model effectively addresses common concerns about AI autonomy, positioning Comp AI as a collaborative partner in achieving robust compliance rather than a fully autonomous system.
Market Imperatives: Revenue, Risk, and the Agentic Era
The strategic timing of Comp AI’s emergence aligns perfectly with profound shifts in the global business and technological landscape. Lewis Carhart eloquently articulated the direct correlation between robust security, compliance, and tangible business revenue. He cited a common scenario where a potential customer might request a SOC 2 report as a prerequisite for finalizing a deal, illustrating how compliance can serve as a significant gatekeeper for market access and business growth, particularly for rapidly scaling startups vying for lucrative enterprise contracts. "What Comp AI automates is much of the work companies traditionally have to do around that process," Carhart noted, emphasizing the platform’s ability to remove critical friction from sales cycles and accelerate overall business development.
The broader cybersecurity and compliance market landscape provides compelling context for Comp AI’s innovative value proposition. The global cybersecurity market size was valued at approximately $172 billion in 2023 and is projected to reach over $420 billion by 2030, exhibiting a robust compound annual growth rate (CAGR) exceeding 13%. Within this expansive market, the governance, risk, and compliance (GRC) software sector alone is anticipated to grow from $12.4 billion in 2023 to over $30 billion by 2028. This sustained growth is primarily fueled by an ever-increasing volume and complexity of regulatory frameworks—including GDPR, CCPA, HIPAA, ISO 27001, and the ubiquitous SOC 2—alongside a persistently evolving and sophisticated threat landscape.
For many organizations, particularly small and medium-sized enterprises (SMEs) and rapidly scaling startups, achieving and maintaining compliance can be a formidable, resource-intensive undertaking. Industry analyses suggest that the average cost of achieving SOC 2 Type 1 compliance can range from $10,000 to $50,000, with Type 2 compliance often costing upwards of $20,000 to $100,000 annually. These figures do not even account for the significant internal staff hours required, which further drains valuable operational resources. This substantial financial and operational burden often diverts critical resources from core product innovation, market expansion, and strategic growth initiatives. Comp AI directly addresses this inefficiency by automating a substantial portion of this complex work, thereby democratizing access to robust compliance for a wider range of businesses and fostering a more secure digital ecosystem.
Navigating the New Wave of AI Security Risks in the Agentic Era
The advent of the "agentic era," characterized by the rapid adoption and deployment of AI agents capable of autonomous or semi-autonomous actions within enterprise systems, presents an entirely new frontier of security risks and compliance challenges. This paradigm shift necessitates a fundamental re-evaluation of traditional security and compliance methodologies. The current wave of intense experimentation and deployment of AI by companies is creating an urgent and unprecedented need for continuous, and potentially autonomous, security and compliance platforms that can keep pace with dynamic AI environments.
Carhart eloquently articulated this emergent threat landscape: "Imagine a company completes its SOC 2 audit and two weeks later deploys a new AI agent that can access customer data, change permissions across an internal system, or introduce a new vulnerability through code deployment. The audit didn’t become invalid; it simply wasn’t designed to tell you in real time what changed afterward." This vivid scenario highlights a critical gap in traditional, periodic compliance frameworks when confronted with dynamic, AI-driven operational environments. The static nature of historical audits is inherently ill-equipped to provide real-time assurance in systems undergoing constant evolution through the continuous deployment and operation of AI agents.
Mariano Fuentes further elaborated on the specific challenges posed by the proliferation of AI agents within enterprise infrastructure. As companies increasingly integrate AI into their core operations, there arises a critical need for granular visibility and unwavering accountability: specifically, proving precisely what an AI agent accessed, what actions it attempted to perform, and whether it operated strictly within its predefined operational boundaries and permissions. Comp AI is directly tackling this complex challenge by building a foundational security layer meticulously focused on permissions management and comprehensive accountability for AI agents. "We’re building toward a security layer that can monitor and validate those kinds of risk more continuously as these systems evolve," Mariano stated. This proactive, continuous monitoring capability is meticulously designed to provide the necessary guardrails and comprehensive audit trails for AI-driven operations, thereby ensuring that the transformative benefits of AI automation do not inadvertently come at the expense of an organization’s security posture or compliance integrity.
Investor Confidence and Strategic Outlook
The substantial Series A funding round, led by prominent venture capital firms Roo Capital and Grand Ventures, reflects a strong and unequivocal conviction in Comp AI’s vision, technological innovation, and execution capabilities. Venture capital firms are increasingly scrutinizing the cybersecurity market for disruptive technologies that can effectively address the escalating complexities of digital threats and the ever-growing burden of regulatory compliance. Investors like Roo Capital and Grand Ventures likely perceive several compelling factors in Comp AI that underpin their investment rationale:
- Experienced Founding Team: The founders’ proven track record, including the invaluable lessons learned from their prior venture, LeapAI, demonstrates resilience, adaptability, and a profound understanding of the critical importance of achieving product-market fit.
- Addressing a Critical Market Need: The pervasive and continuously growing challenge of cybersecurity compliance, significantly exacerbated by the rapid adoption of AI, presents a vast and largely untapped addressable market for innovative solutions.
- Innovative Technology: Comp AI’s agentic AI platform and its pioneering AI-powered penetration testing offer a truly differentiated approach compared to earlier generations of GRC platforms (e.g., Vanta, Drata). Crucially, Comp AI’s technology is specifically tailored to address the unique complexities and novel risks introduced by the widespread integration of AI systems into enterprise operations.
- Strategic Positioning: Comp AI is not merely automating existing, manual compliance tasks; it is actively building foundational infrastructure for the "next generation" of security in an AI-first world. This strategic positioning places the company as a critical, foundational layer for future enterprise operations, capable of adapting to emerging threats and regulatory landscapes.
The $34 million Series A capital is primarily earmarked for aggressive product expansion. This will likely involve significantly enhancing the platform’s existing capabilities, developing new AI agents to cover an even broader spectrum of compliance frameworks and security tasks, and expanding its cutting-edge penetration testing functionalities. Furthermore, this substantial investment will support scaling the company’s engineering, product development, and sales teams, thereby enabling Comp AI to accelerate its market penetration, broaden its geographic reach, and serve a larger and more diverse client base across various industries.
Broader Implications for Cybersecurity and Enterprise Resilience
Comp AI’s successful funding round and its innovative approach carry significant implications for the broader cybersecurity industry and for enterprises grappling with the accelerating pace of digital transformation:
- Democratization of Compliance: By automating historically complex and costly compliance processes, Comp AI has the potential to make robust security and regulatory adherence accessible to a much wider array of businesses, ranging from nascent startups to established enterprises. This accessibility can level the playing field, foster greater trust across the digital ecosystem, and reduce barriers to market entry for innovative companies.
- Accelerating Innovation: By significantly reducing the burden of manual compliance tasks, Comp AI effectively frees up critical engineering, operational, and financial resources within organizations. These resources can then be strategically reallocated towards core product development, market-driven innovation, and initiatives that drive sustainable strategic growth, thereby fostering a more dynamic and competitive business environment.
- Shifting Security Paradigms: Comp AI’s unwavering focus on continuous, AI-driven monitoring and its direct response to the "agentic era" foreshadows a future where cybersecurity is not merely a periodic audit or a reactive measure, but rather an omnipresent, adaptive, and intelligently integrated layer embedded deeply within all enterprise operations. This proactive, intelligent stance is absolutely crucial in an environment where digital threats and system configurations are in a state of constant, rapid flux.
- The Future of Audit: While Comp AI’s platform is designed to augment and empower rather than replace independent auditors, it will undoubtedly fundamentally transform the nature of audits. The focus will shift from laborious, manual evidence gathering to the rigorous verification of the efficacy and integrity of automated compliance systems, providing auditors with access to more comprehensive, real-time data and a more granular understanding of an organization’s continuous security posture.
- Responsible AI Deployment: By meticulously integrating human oversight and placing a strong emphasis on granular permissions and robust accountability for AI agents, Comp AI actively contributes to the development and promulgation of responsible AI practices. This ensures that the transformative power of artificial intelligence is harnessed securely, ethically, and in a manner that aligns with an organization’s values and regulatory obligations.
In a world increasingly reliant on artificial intelligence, the security and compliance landscape is undergoing a profound and irreversible transformation. Comp AI, with its substantial new funding and pioneering agentic platform, is exceptionally well-positioned to lead this charge, offering enterprises a sophisticated yet accessible solution to navigate the inherent complexities of digital trust in the rapidly evolving, AI-driven future. The company’s journey from recognizing a significant market pain point to securing substantial investment powerfully underscores the critical and growing need for intelligent, automated solutions in the perpetually evolving realm of cybersecurity and compliance.
